Hi,
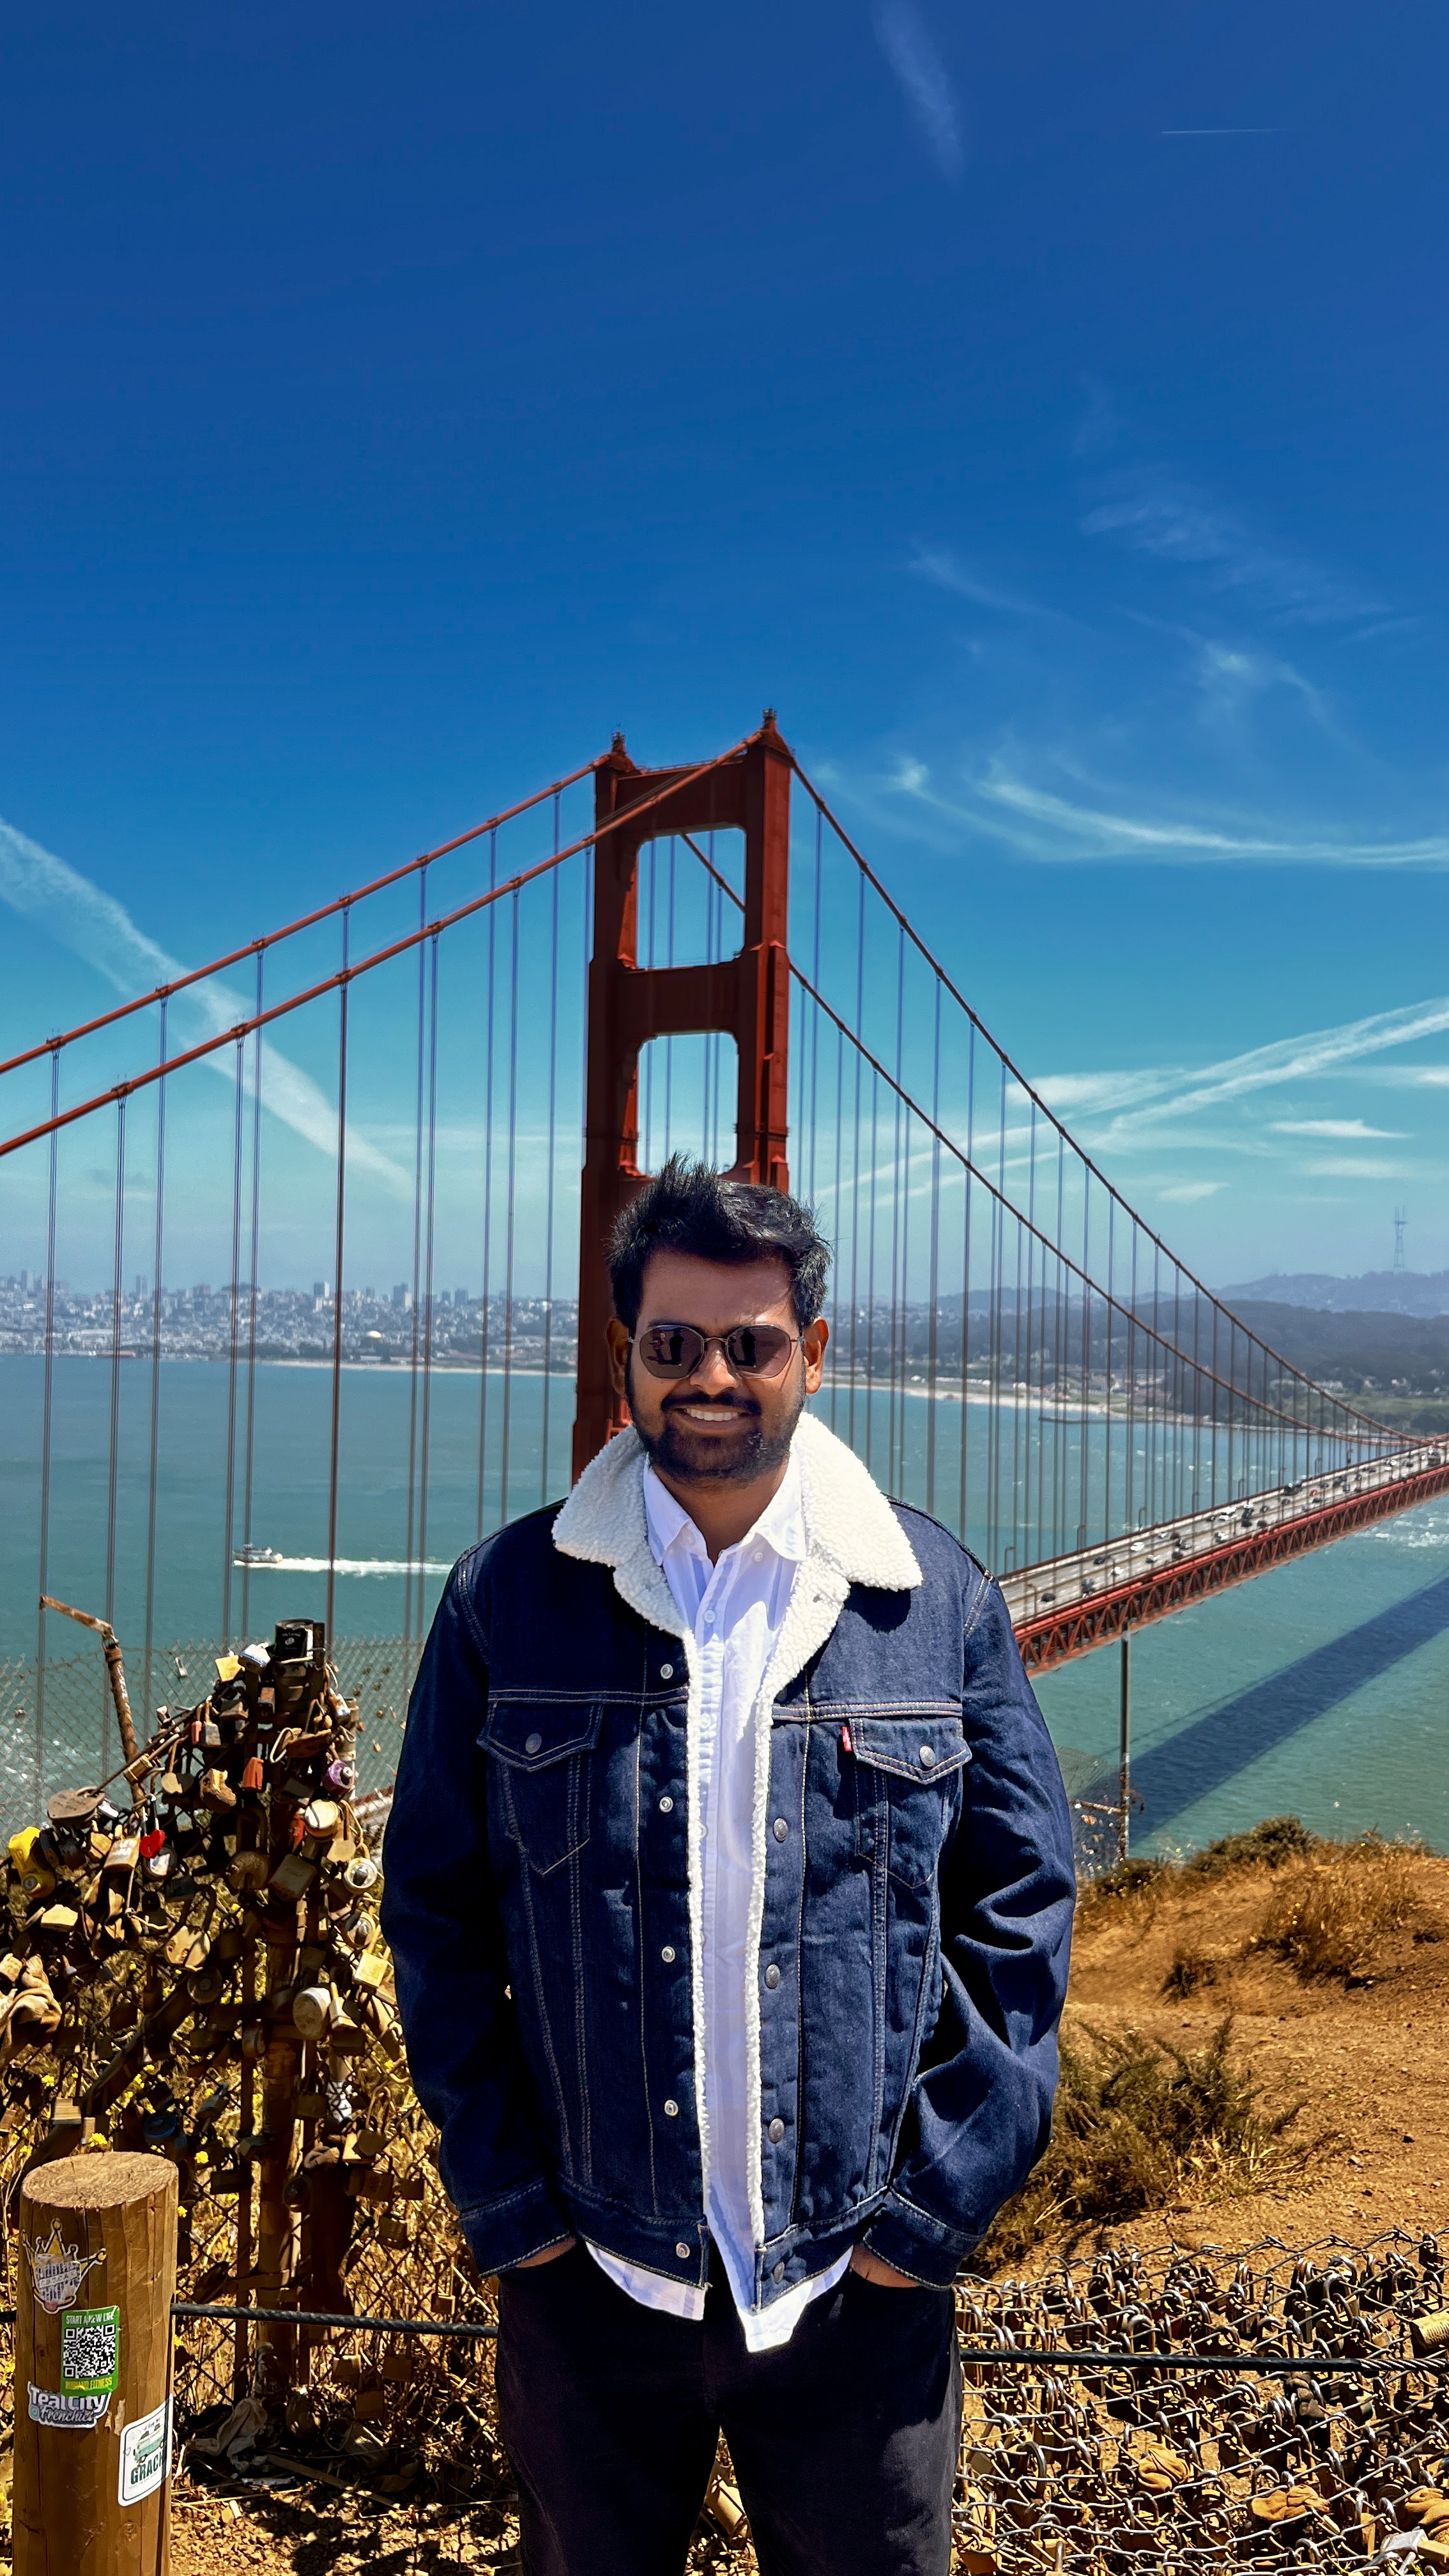
I'm Harsh Akshit
AI Security Researcher
Cybersecurity professional specializing in AI Safety, LLM Jailbreaking, and Vulnerability Management
Cybersecurity professional specializing in AI Safety, LLM Jailbreaking, and Vulnerability Management
Cybersecurity professional with strong focus in AI and Application security, vulnerability management, and innovative security solutions. Passionate about travelling and exploring diverse cultures. Featured in Google Bug Hunter Hall of Fame. Known for identifying critical risks and enhancing digital resilience. Want to discuss about security of your product, let's chime in sometime.
Academic journey in cybersecurity and computer science
Advanced studies in cybersecurity, risk assessment, and security architecture. Focus on emerging threats in AI and cloud security.
Bachelor's degree, Computer Science. Built a strong foundation in programming, algorithms, and system design.



Recognition
Recognized for discovering and responsibly disclosing critical security vulnerabilities in Google's infrastructure.
Recognition
Recognized for discovering and responsibly disclosing a security vulnerability in LangChain.
NAMER - North America
Building secure systems and advancing security research across AI and traditional application security.
• Researching attacks against agentic AI systems, spanning malicious and backdoored agent
skills, MCP connectors, and autonomous tool-use workflows, including prompt injection,
sleeper skills, privilege misuse, and data exfiltration
• Building dynamic analysis behind SkillTracer, detonating agent skills in an instrumented
sandbox across multiple models to compare stated intent against actual runtime behavior,
with findings scored via AIVSS and mapped to the OWASP Agentic Top 10
• Converting research into detection and governance logic for Metano's security control
plane, giving defenders runtime visibility into agent activity that EDR and SIEM miss, and
publishing threat research on emerging agentic attack patterns

• Researching emerging attack paths across AI agents, LLM applications, MCP connectors, and
autonomous tool-use workflows, including prompt injection, tool abuse, permission misuse,
and data leakage
• Designing evaluation pipelines, adversarial test cases, attack simulations, and benchmark
datasets, converting research findings into detection logic for the Wingback platform
• Prototyping product capabilities for runtime monitoring, policy enforcement, and agent
behavior analysis, and contributing to threat intelligence and customer-facing research
• Conducting in-depth research on adversarial attacks against large language models (LLMs),
focusing on jailbreaks and prompt injection techniques
• Explored security risks associated with Model Context Protocol (MCP) and Agentic AI,
utilizing red-teaming methodologies
• Contributing to thought leadership blogs and internal reports, enhancing the community's
understanding of AI/ML security threats
• [INFO-I 230 Analytical Foundation of Cybersecurity] Assisted in
delivering over 24 foundational security concepts, including cryptography, risk assessment,
access control, and secure system design, to undergraduate students. Provided technical
support to over 60 students, graded assignments, and facilitated 15+ lab sessions,
significantly improving students' practical understanding of foundational cybersecurity
concepts
• [CSCI A-541: Computing & Technology Bootcamp] Assisted in delivering a
high-level introduction to computing, networking, cybersecurity, AI, and cloud technologies
for students from non-technical backgrounds. Supported course instruction through clarifying
technical concepts, guiding discussions, grading assignments/exams, and helping students
build foundational knowledge to engage in policy, business, and legal decision-making around
technology
• Protected 2M+ consumers across 80+ projects through comprehensive security assessments
• Conducted application security testing (AppSec), software composition analysis (SCA), and
static application security testing (SAST)
• Performed vulnerability testing and compliance audits for enterprise clients
• Worked with notable clients including CVS Healthcare, Global Payments, nCino, Prometric,
Intuit, and others
Bengaluru, Karnataka, India
Bengaluru, Karnataka, India
Hyderabad, Telangana, India
Noida, Uttar Pradesh
Published work on emerging security threats and vulnerability analysis.
Metano Labs research on the self-update trust gap in AI agent skills: 50+ marketplace skills carry silent auto-update paths, downloaded 28k+ times, so a point-in-time audit score gets carried forward to code nobody reviewed.
Read more →Metano Labs research on unclaimed dependencies in public AI agent skills: they instruct agents to install packages that were never published, and whoever registers the name first inherits code execution on every machine told to install it.
Read more →A complete guide to the React2Shell vulnerability (CVE-2025-55182) - the critical 10/10 RCE flaw that scared the internet.
Read more →Low-interaction honeypot to detect LLMjacking attacks campaigns that scan for exposed AI infrastructure to steal compute resources.
View on GitHub →Deep dive into the latest jailbreak techniques observed in the wild and their implications.
Read more →In-depth analysis of payment security vulnerabilities and exploitation techniques.
Read more →Vulnerabilities I reported that were assigned CVE IDs.
A missing permission check on the image preview endpoint let any user with Wagtail admin access preview any image, regardless of their permissions.
View advisory →The Documents and Images chooser's chosen endpoint listed items the user had no choose permission for, exposing their names, filenames, and URLs.
View advisory →Comprehensive skill set across AI security, application security, and compliance frameworks.
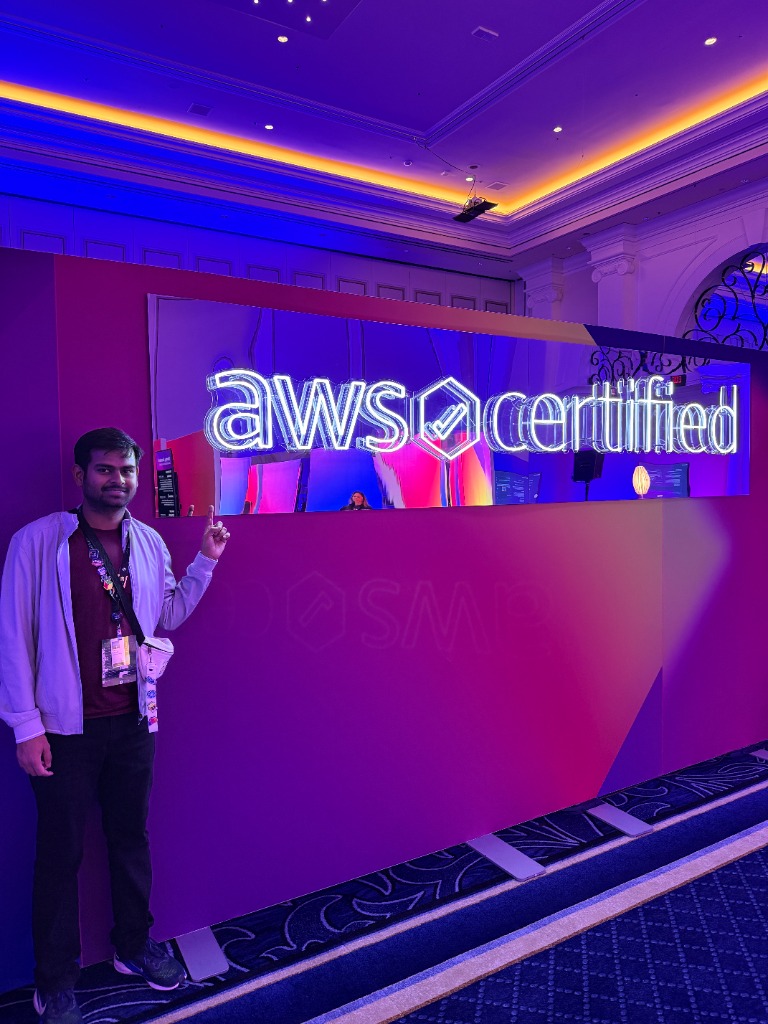
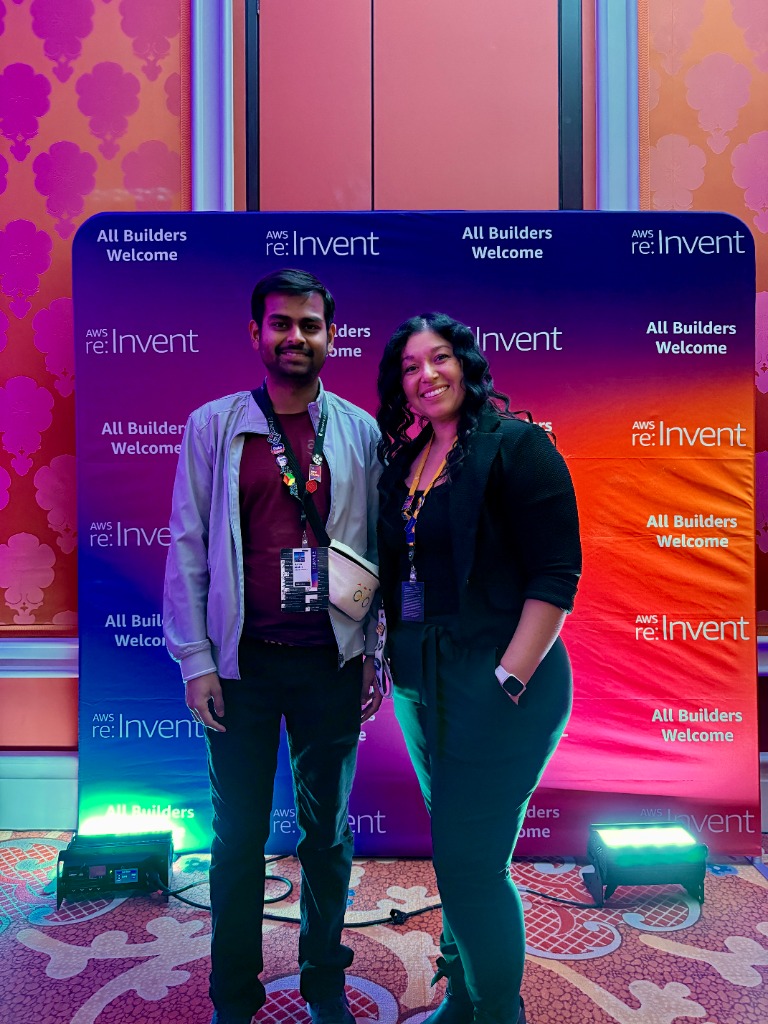
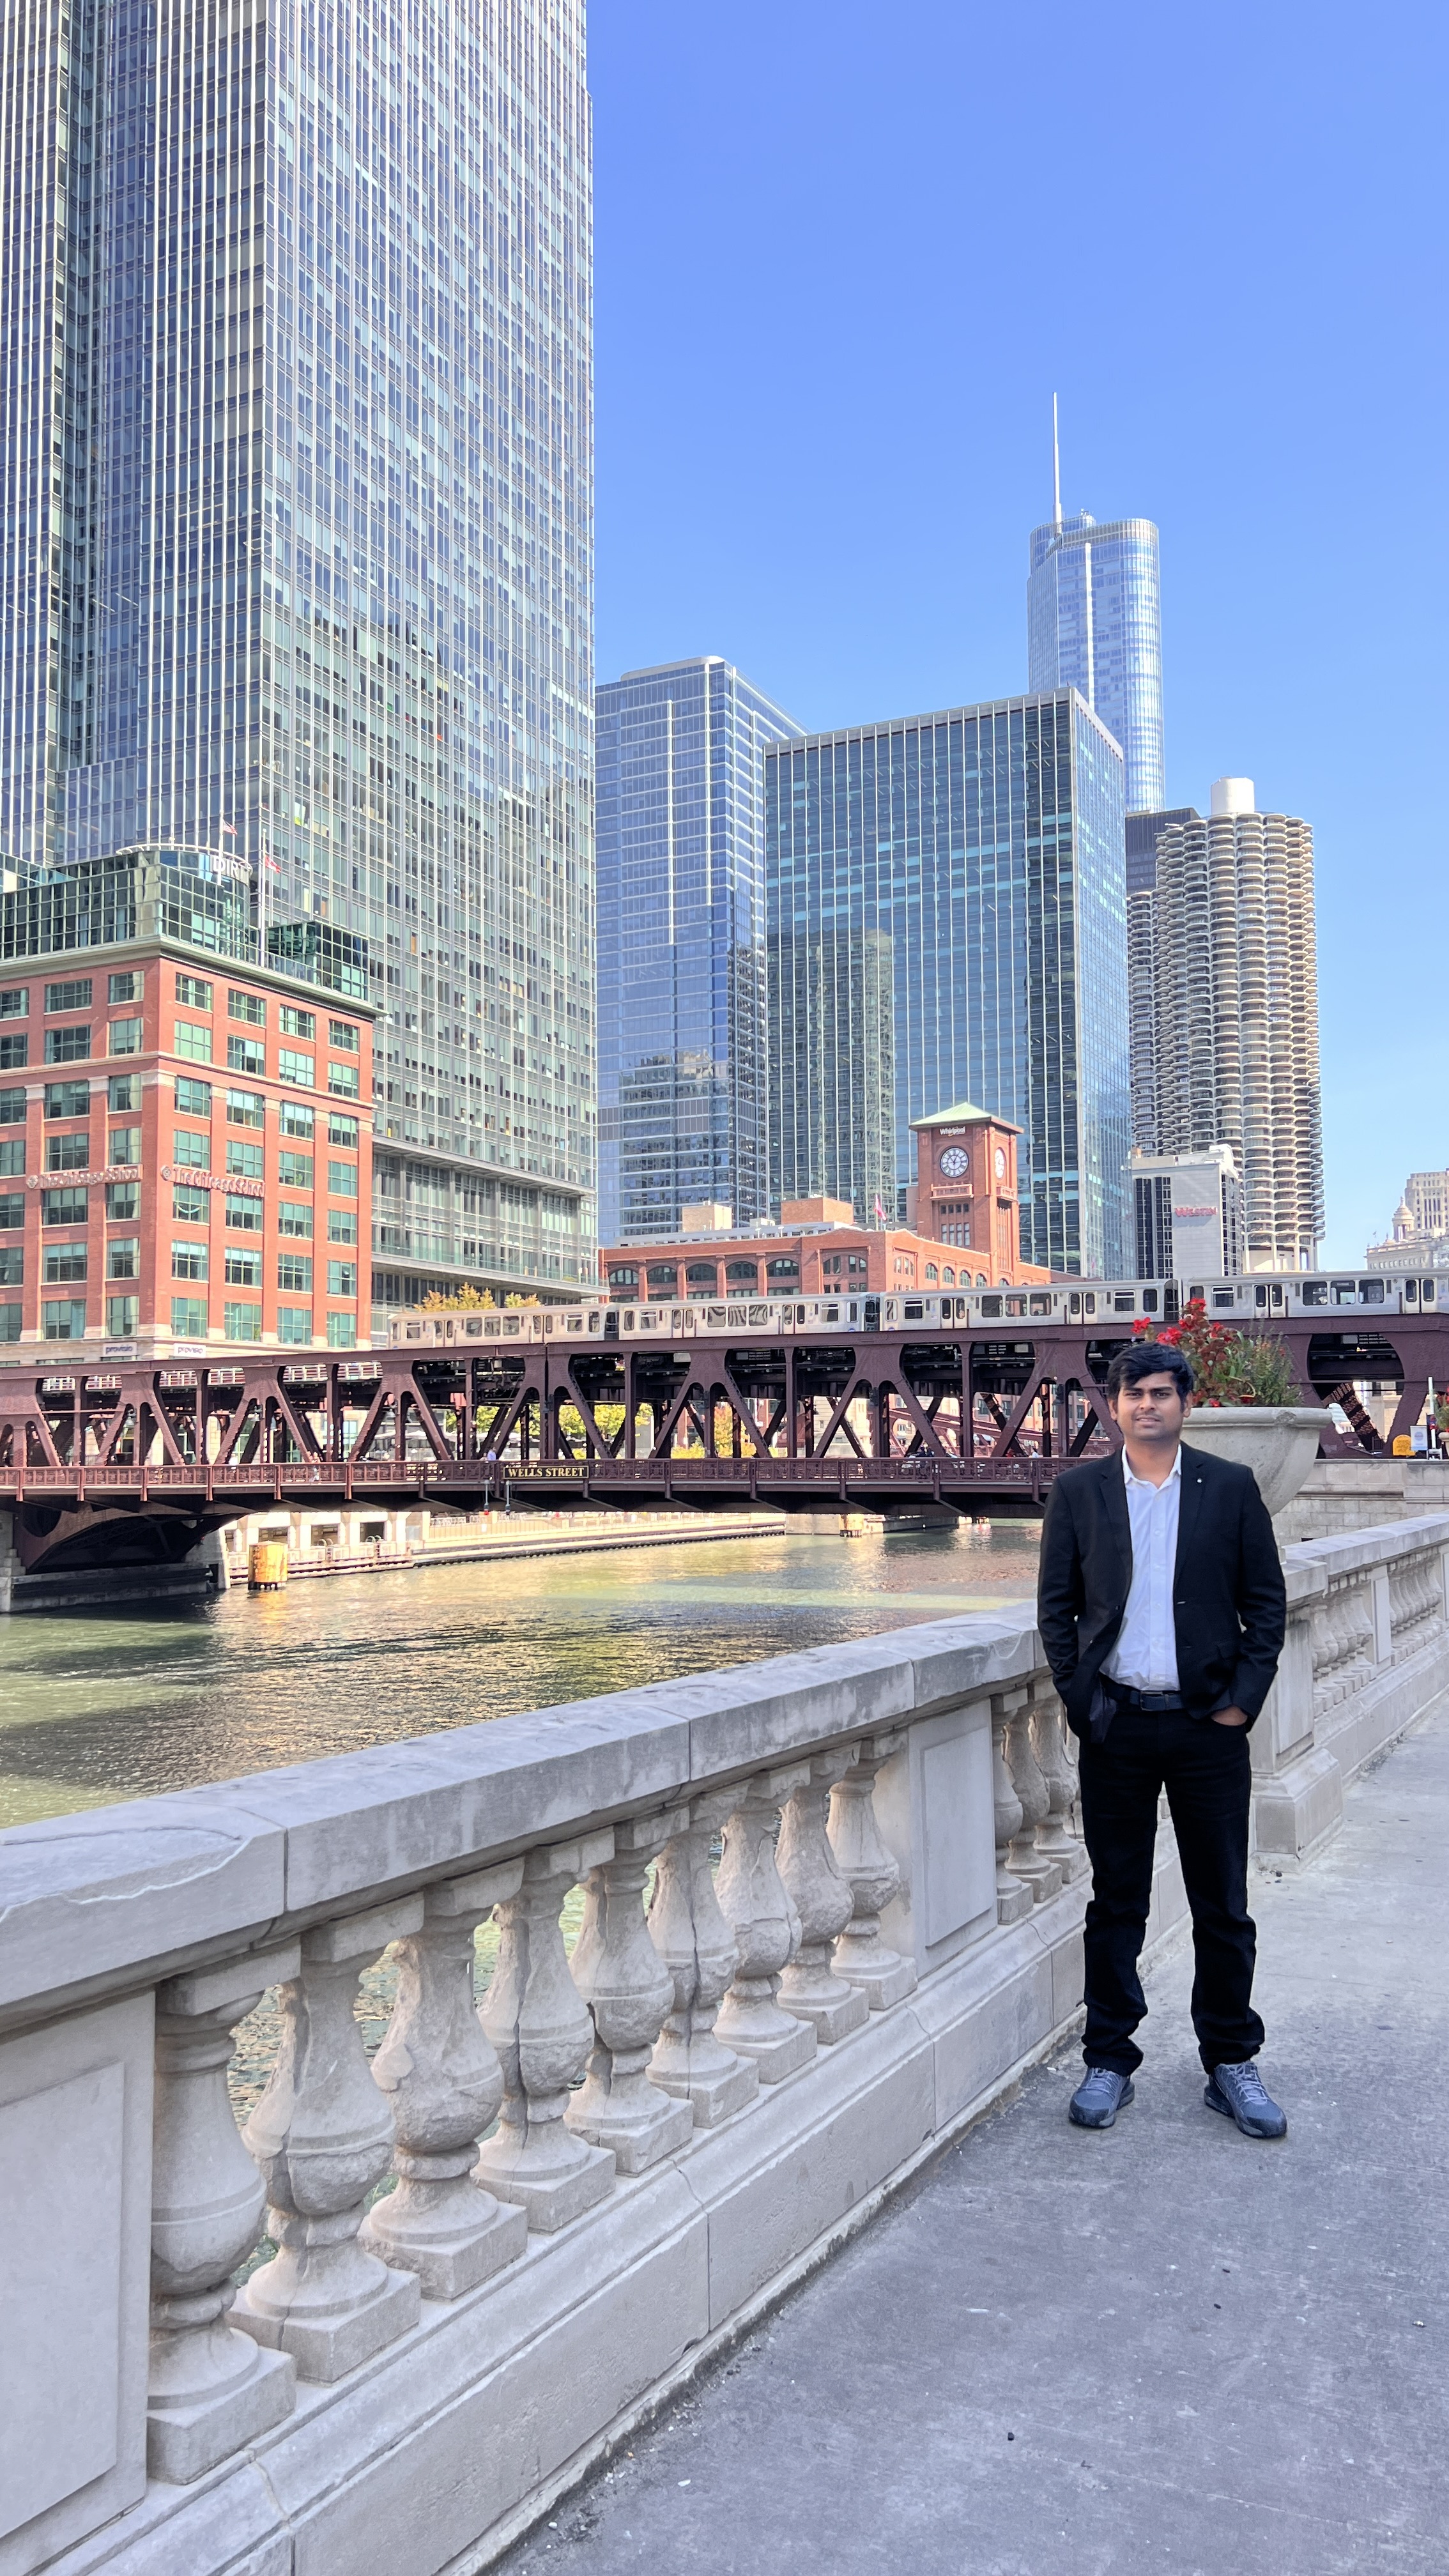
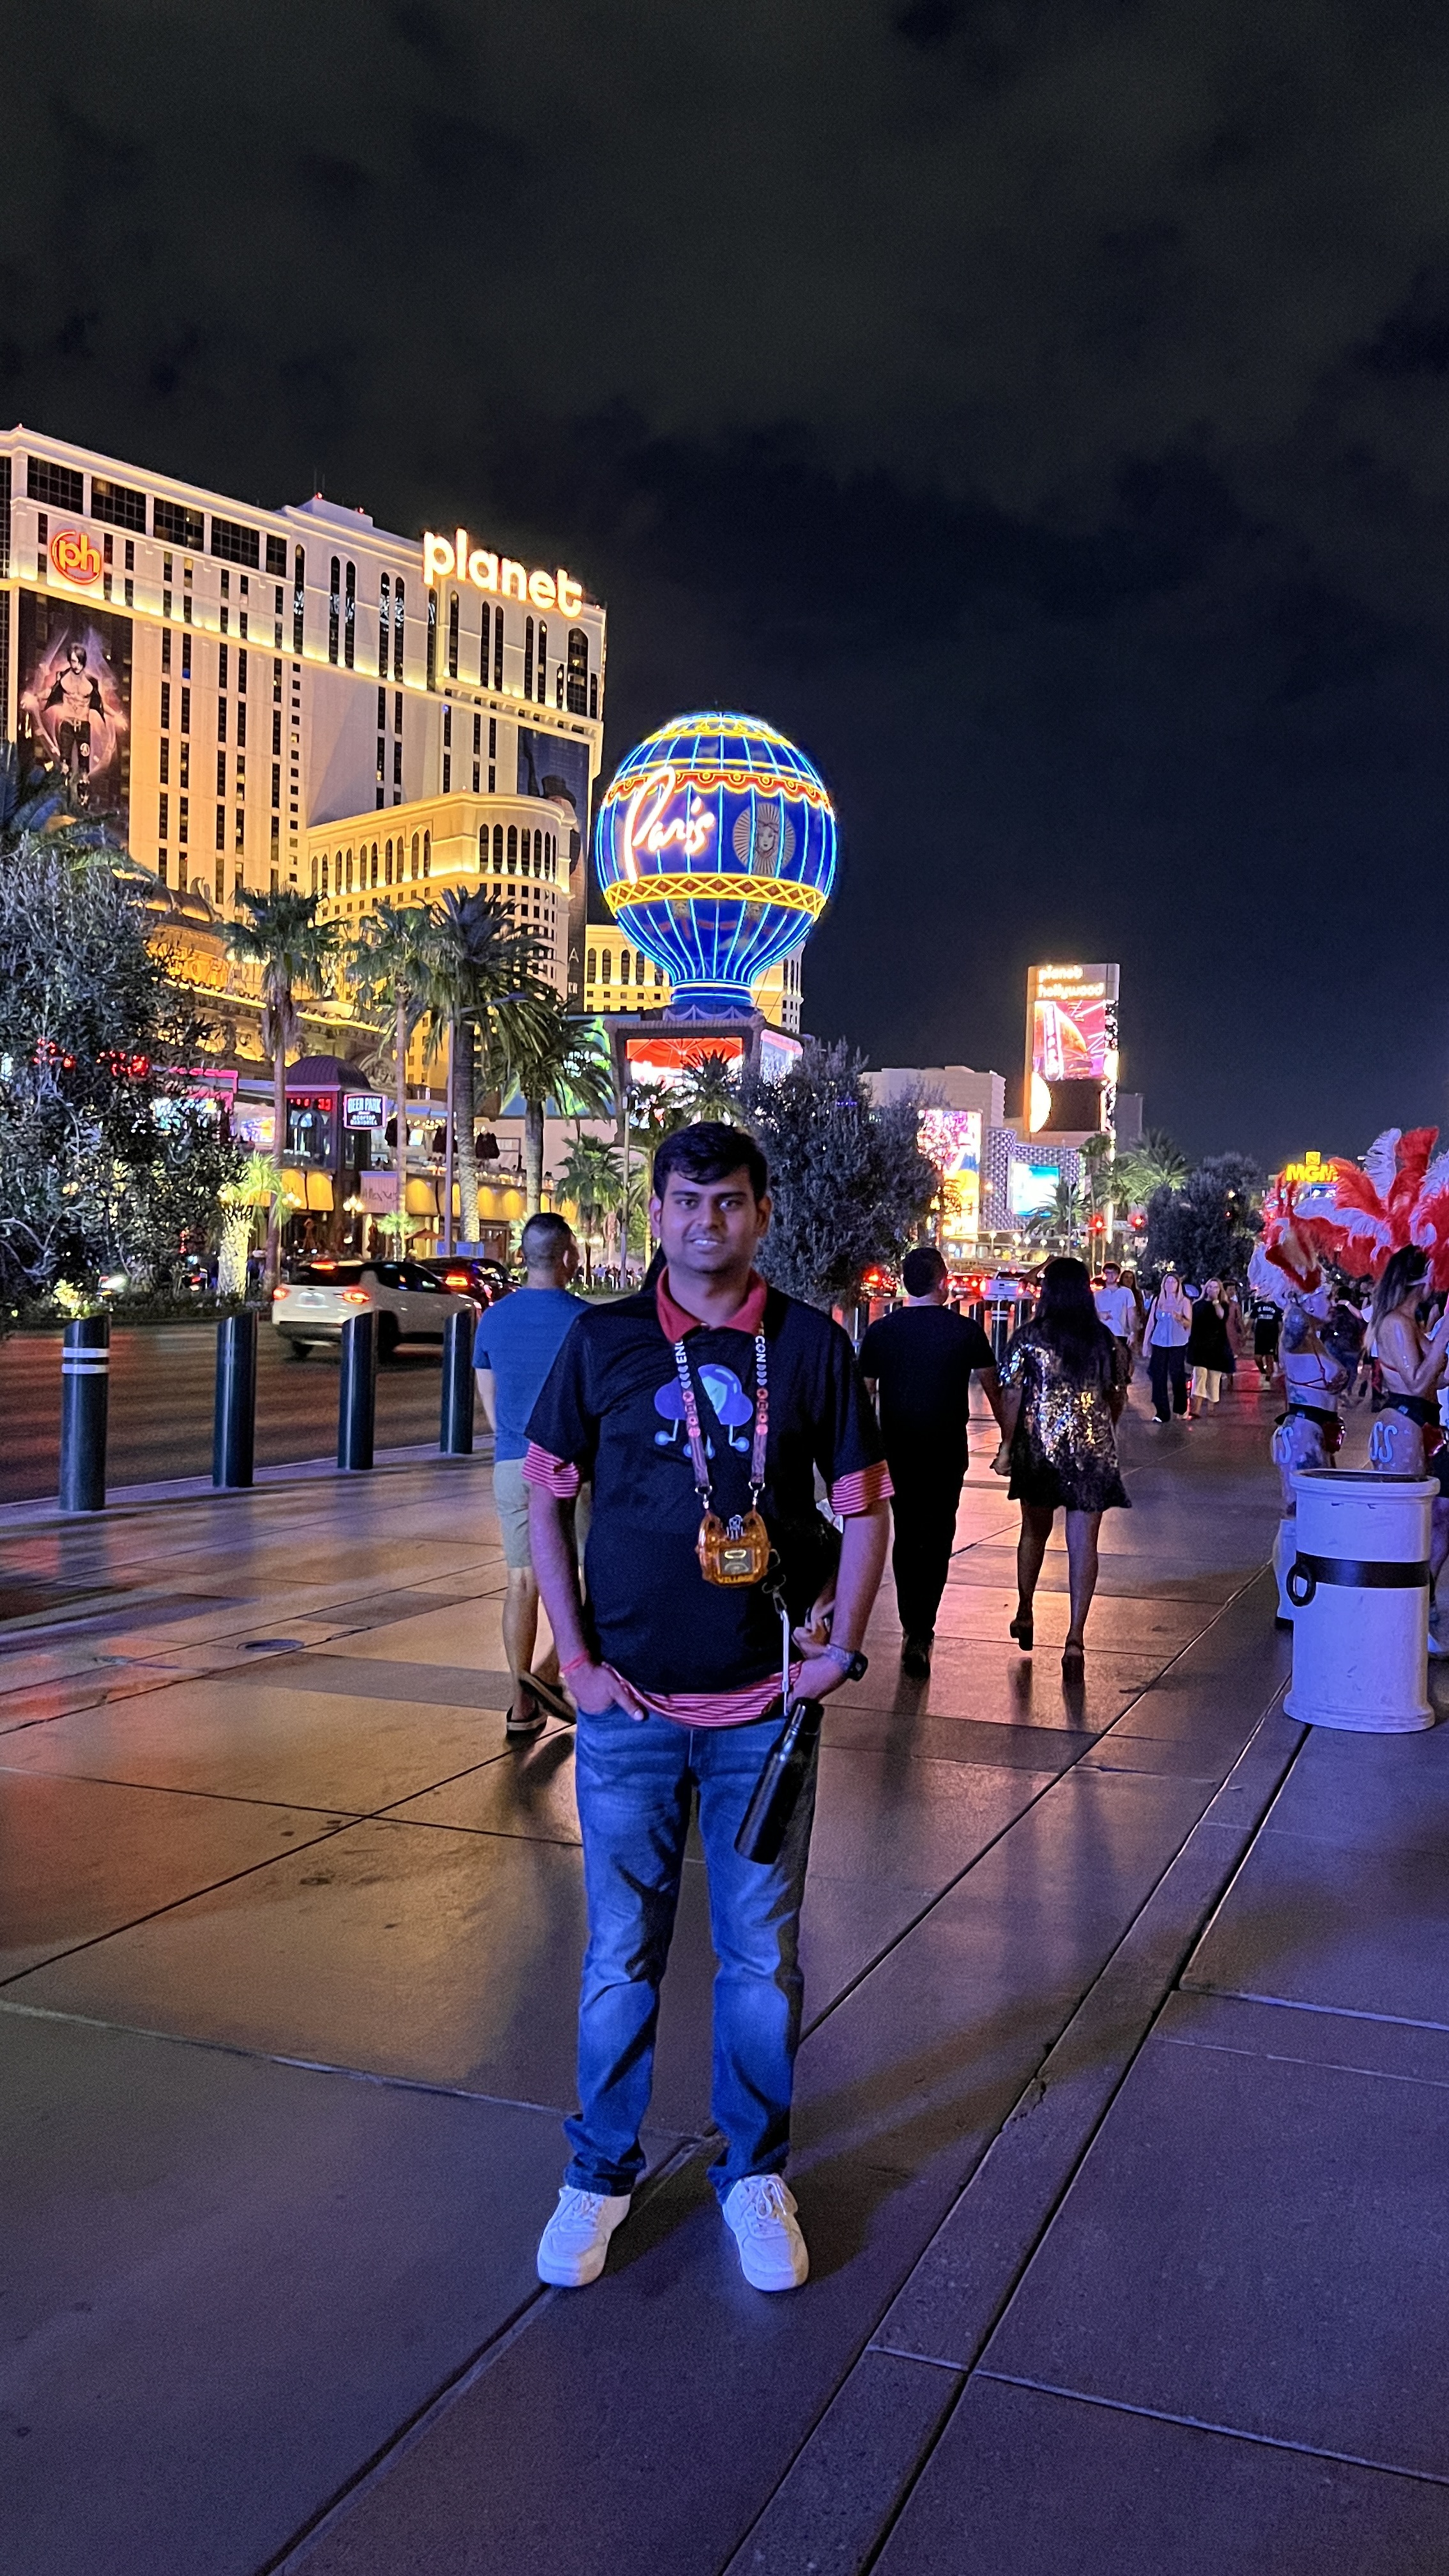
Connecting with the cybersecurity community at events and meetups worldwide
Feel free to reach out for collaborations, opportunities, or just to chat about security.

